 pypiron


Host private packages and cache PyPI behind one ultra-fast index.
Get started · Deploy on cloud storage

- 100× faster than other self-hosted PyPI servers. 8,288 installs/s on 2 vCPU.
- Blocks 72% of malicious releases by default.
- Local disk, S3, GCS, and Azure.
- Scale without a database or coordinator. Add nodes to one bucket.
- Survives a region or cloud outage.
- Real clients. Real clouds. All 17 million PyPI files.
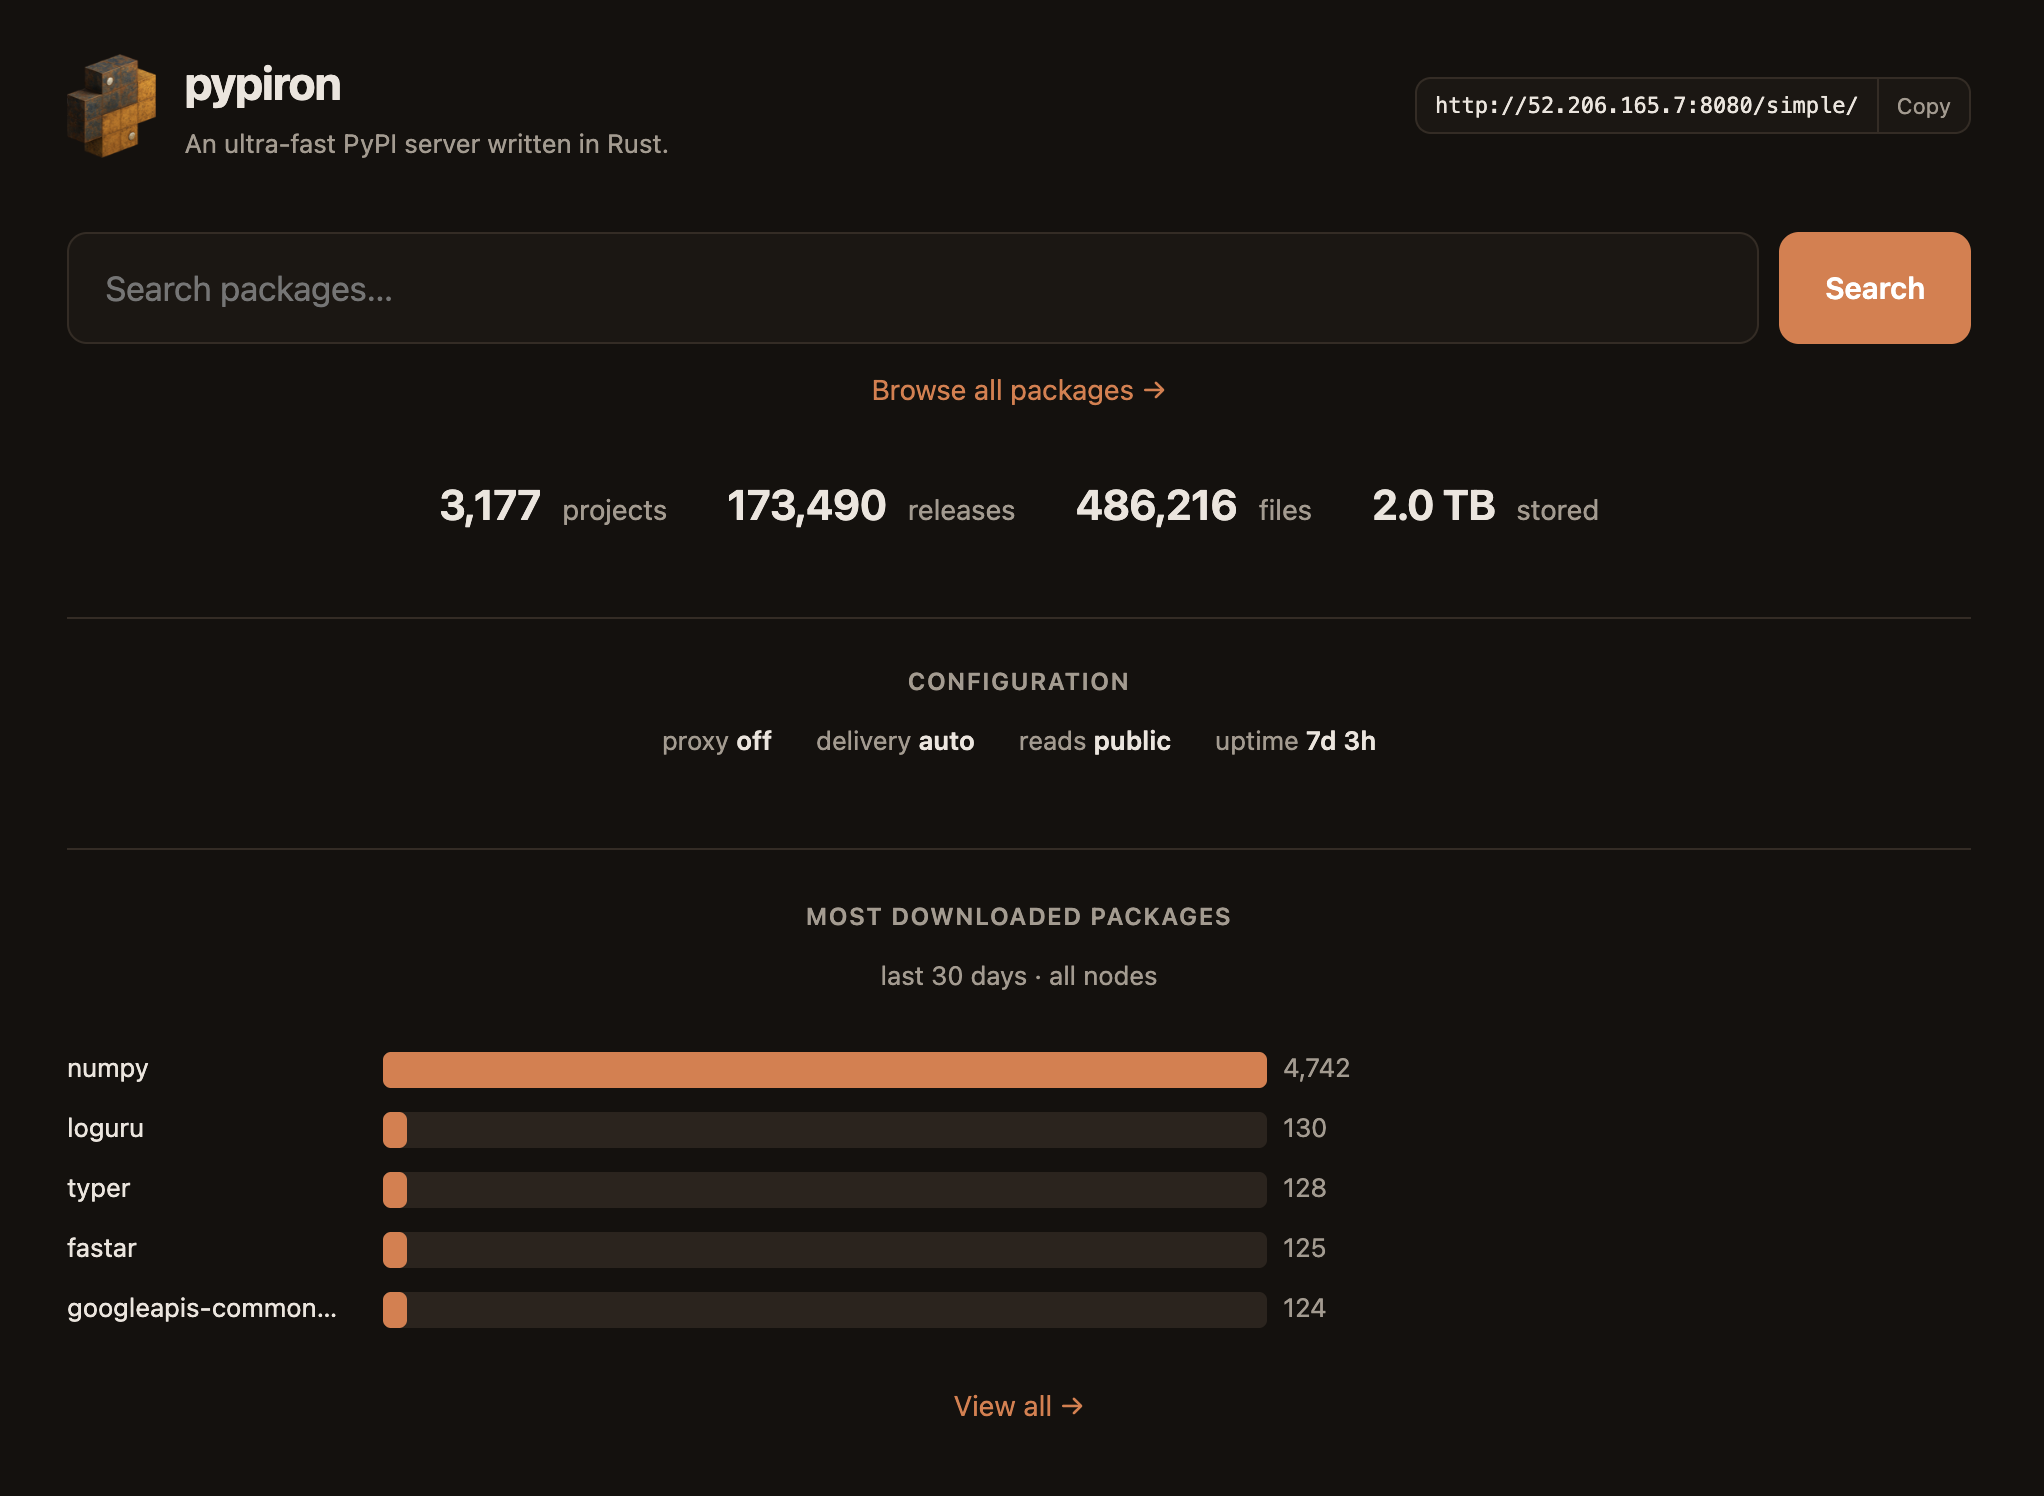
- Web dashboard with package pages and search.
- Health checks and Prometheus metrics built in.
Start pypiron
With uv installed,
replace your-admin-password and run:
pypiron is now running at http://localhost:8080. The admin username is
admin; the password is the one you chose.
Docker:
docker run -p 8080:8080 -e PYPIRON_ADMIN_PASS='your-admin-password' ghcr.io/blackthorn-interstellar/pypiron:latest
Publish and install packages · Deploy on cloud storage · Migrate from another server
Feature comparison
| Feature | pypiron | bandersnatch | pypiserver | pypicloud | devpi | proxpi | |
|---|---|---|---|---|---|---|---|
| Easy setup | ✅ | — | ✅ | — | — | ✅ | |
| Fast | ✅ | ✅ | — | — | — | — | |
| Private packages | ✅ | — | ✅ | ✅ | ✅ | — | |
| PyPI proxy | ✅ | — | — | ✅ | ✅ | ✅ | |
| Sync mirror | ✅ | ✅ | — | — | — | — | |
| Cooldown | ✅ | — | — | — | — | — | |
| Malware blocking | ✅ | — | — | — | — | — | |
| No dependency confusion | ✅ | — | — | — | ✅ | — | |
| Vulnerability audit | ✅ | — | — | — | — | — | |
| Scales, no database | ✅ | ✅ | — | — | — | — | |
| Multi-region failover | ✅ | — | — | — | ✅ | — | |
| Web GUI | ✅ | — | — | ✅ | ✅ | — | |
| Download stats | ✅ | — | — | — | — | — | |
| Storage | Disk | ✅ | ✅ | ✅ | ✅ | ✅ | ✅ |
| AWS S3 | ✅ | ✅ | — | ✅ | — | — | |
| GCS | ✅ | — | — | ✅ | — | — | |
| Azure Blob | ✅ | — | — | ✅ | — | — | |
Security
- Blocks known PyPI malware. OSV blocking plus a release cooldown.
- Private names stay private. They never fall through to public PyPI.
- Control which public packages install. Set one approval list for every client.
- Air-gapped deployments. Serve approved packages without internet access.
- Vulnerability audit. Affected public packages, ranked by downloads.
Gauntlet testing
- Eight real clients. uv, pip, poetry, pdm, pipenv, hatch, flit, and twine.
- Every PyPI file. All 17 million, checked against ground truth.
- Killed mid-write. Crash sweeps, fleet chaos, and hostile upstreams.
- Fuzzed nightly. Simulated and model-checked.
- Security-audited by frontier models. The same models that built it.
See the full testing gauntlet.
Going further
- Publish and install — private packages and the PyPI cache
- Deploy on cloud storage — S3, GCS, or Azure
- Migrate — move from pypicloud, devpi, Artifactory, or Nexus
- How pypiron works — storage, caching, access, and recovery
- Configuration — every flag and its
PYPIRON_*env var - Compare servers — benchmarks and when to choose something else
- For AI agents — decide, configure, and verify
Contributing — Humans Need Not Apply
pypiron was built by AI coding agents from Anthropic, OpenAI, SpaceXAI, and Moonshot — and that's how it stays. All development is done by AI coders, for security and consistency: human-developed code is a security risk, and we don't accept it. Humans are welcome to open issues and contribute documentation.
License
MIT — see LICENSE.